HoneyLabs

Blog

Field notes from running honeypot sensors at scale.

2026-09-23

Analyzing 7 million Go TLS handshakes to see which Go versions scan the internet

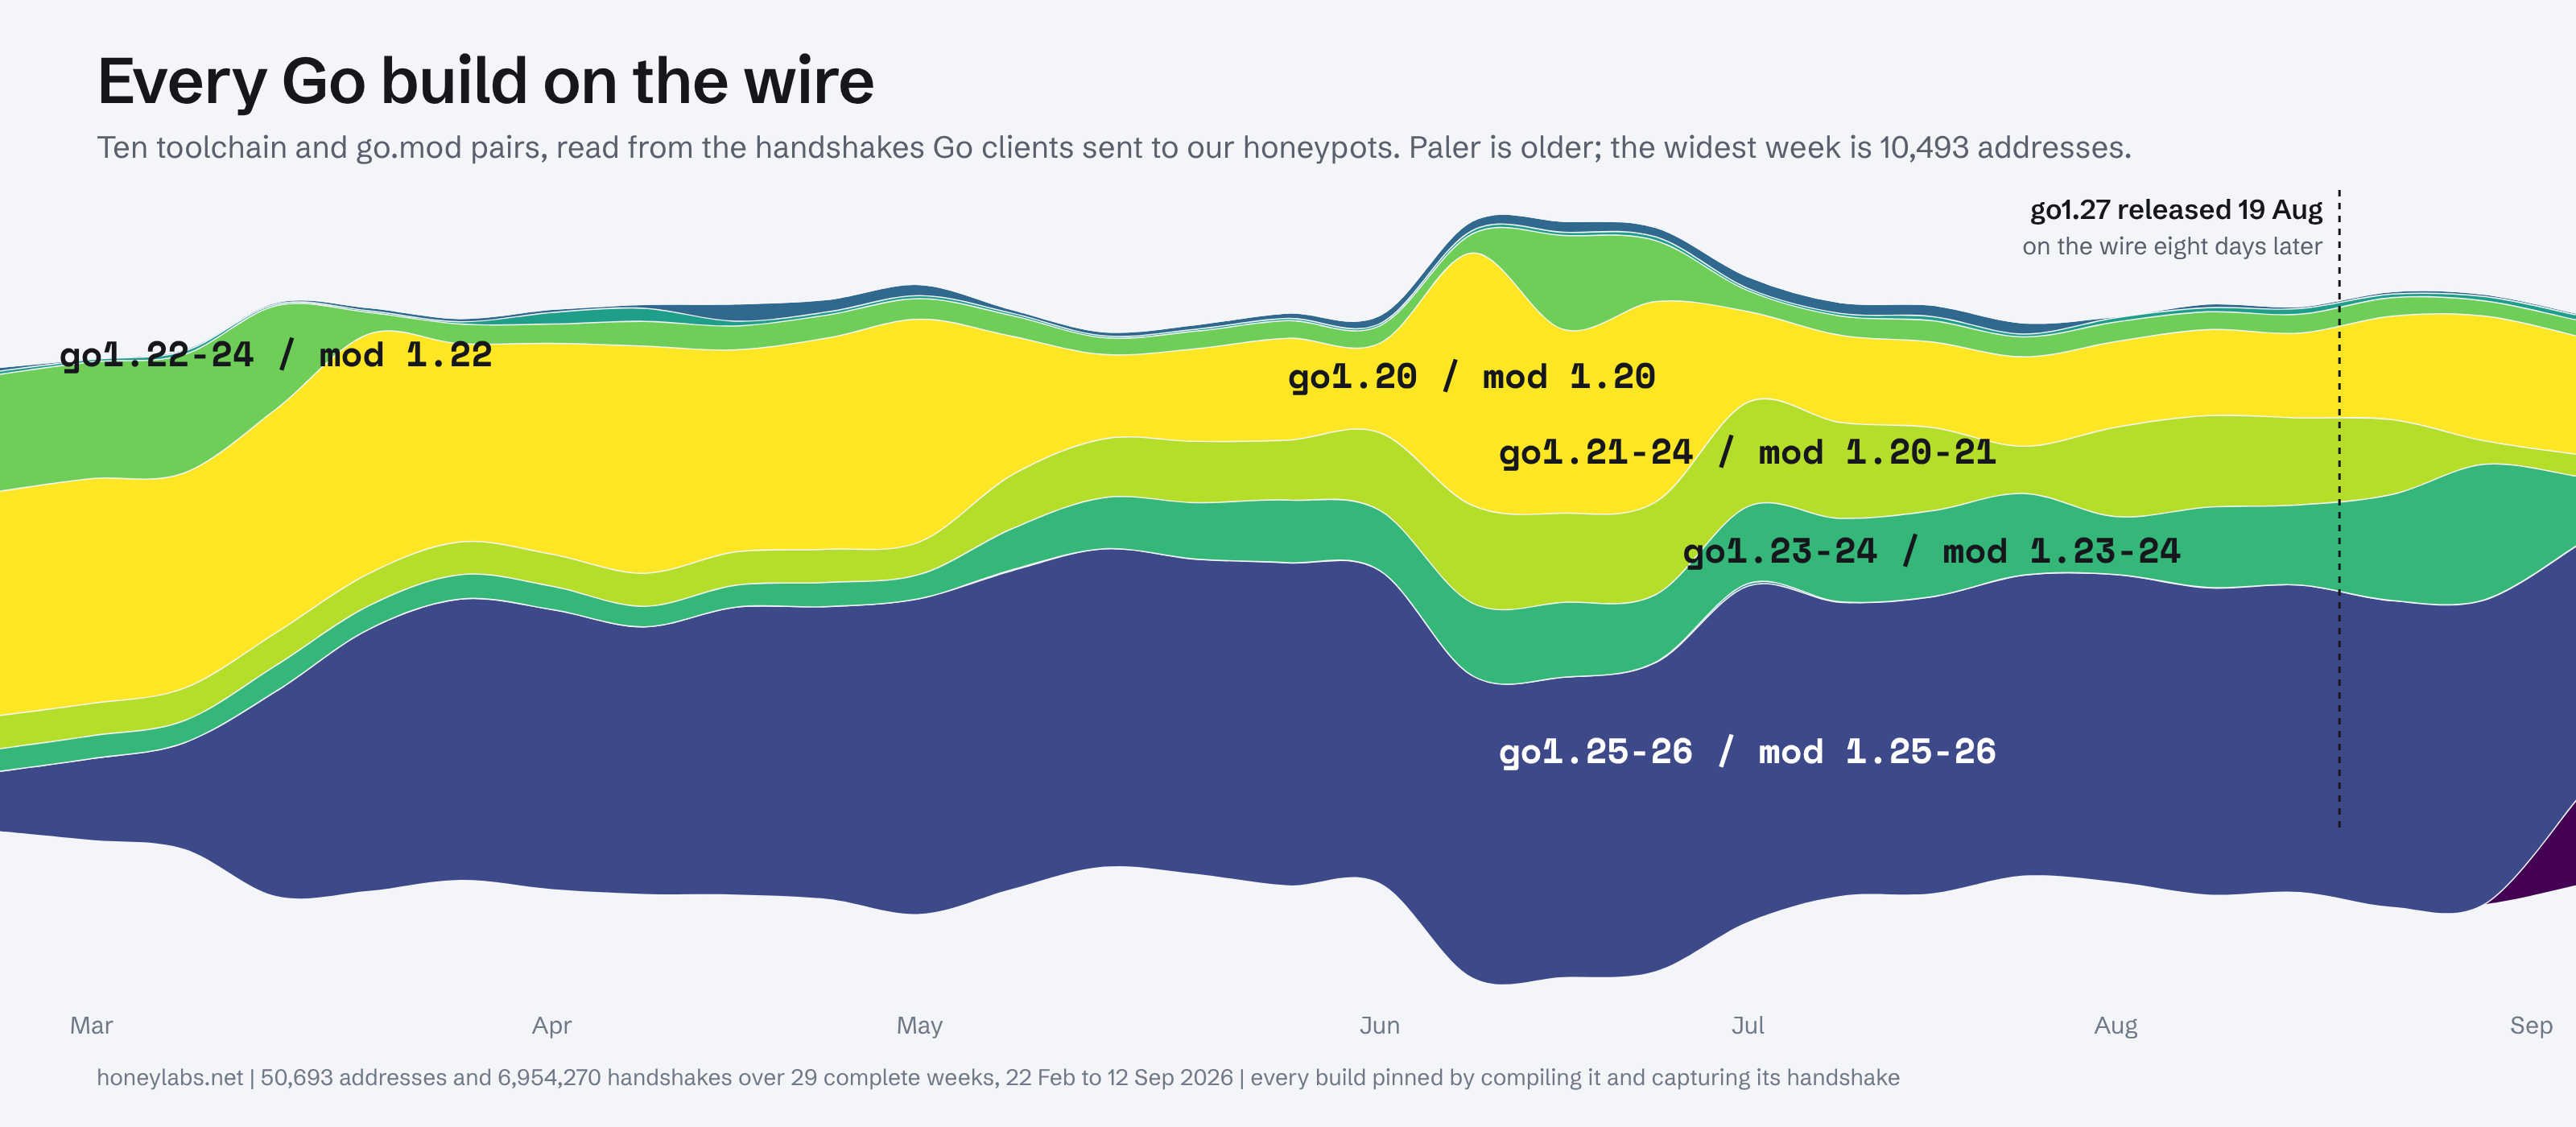
Every handshake here came from a Go client that scanned one of our internet honeypots. Since Go 1.21 the toolchain takes its crypto/tls defaults from the go directive in go.mod, so each ClientHello carries the module's era rather than the compiler's. Measured with 36 lab builds against 6,954,270 such handshakes from 50,693 addresses: the share on a directive of 1.22 or older fell from 81 to 30 percent between March and May, only 4 percent of them send a Go user-agent, and a go 1.23 directive on a modern toolchain gets no post-quantum key exchange at all.

New research, by email

Get new HoneyLabs posts by email as they publish: research write-ups, plus threat reports on port movers, KEV and recent CVE probes, and the attack paths worth grepping your own logs for. Here is a recent threat report.

Double opt-in: we send one confirmation email and nothing else until you click it. Unsubscribe in one click, any time.